
Core Lightning warns attackers are targeting unpatched Bitcoin nodes

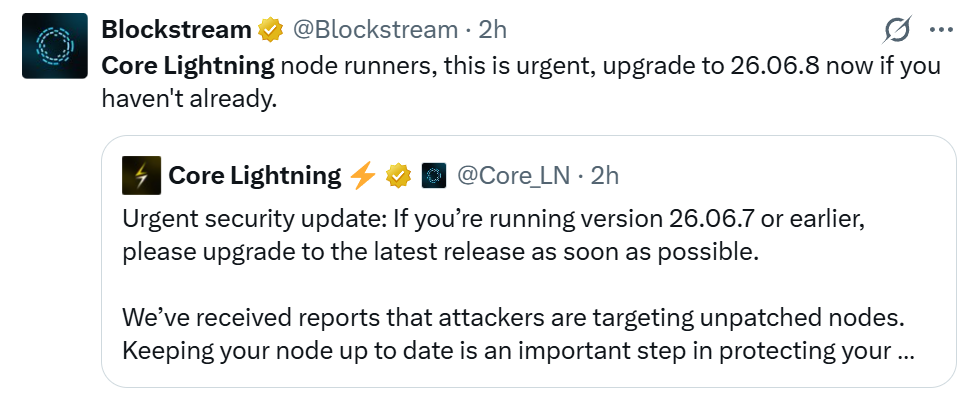
The team behind Core Lightning, an open-source node software for the Bitcoin Lightning Network, has urged operators running older versions to upgrade immediately after receiving reports of attackers targeting unpatched nodes.
Core Lightning did not specify which vulnerabilities attackers were targeting or the potential impact. Cointelegraph reached out to Core Lightning for comment.
On Sept. 16, Core Lightning said it was investigating reports of a potential issue affecting experimental features in Core Lightning that could impact user funds. It then released version 26.06.8 around six days later.
The Sept. 22 update delivered bug fixes alongside patches for “vulnerabilities responsibly reported by a number of sources.” The release notes credit the Bitcoin Red Team and 12 other named individuals and groups, along with anonymous reporters.
Some of the fixes addressed flaws that could crash senders’ nodes, requests that could exhaust memory in its REST interface and a channel-closing bug that could cause users to lose funds to a penalty, according to the changelog.
However, the release deliberately withheld some tests to make it harder for attackers to reverse-engineer and exploit vulnerabilities while operators upgraded.
In August, Core Lightning said it was working on a coordinated fix after assessing a high volume of AI-generated Common Vulnerabilities and Exposures (CVE) reports over recent weeks.
Two days later, it released 26.06.7 to address the confirmed vulnerabilities.
Disclaimer: The content of this article solely reflects the author's opinion and does not represent the platform in any capacity. This article is not intended to serve as a reference for making investment decisions.
You may also like
Aave Prints Enormous 68% Volume Increase: What's Behind It
Nvidia rises over 2%, sets another record high
Data: 500 millions USDT transferred out of a certain exchange
BUZZ-Verastem shares rise on positive ovarian cancer drug trial results
Crypto prices
More


